

Set up Snowflake
Snowflake lets people authorize access through Snowflake’s sign-in page, including multi-factor authentication required by their organization. It stays unavailable until a Cassidy administrator completes setup.1
Register an OAuth application in Snowflake
Ask a Snowflake administrator to follow Snowflake’s OAuth security integration
reference to create an
OAuth security integration and retrieve its client ID and client secret.In Cassidy, open Organization settings → Connectors, find Snowflake,
and select Set up from its menu. Configure the Snowflake integration with: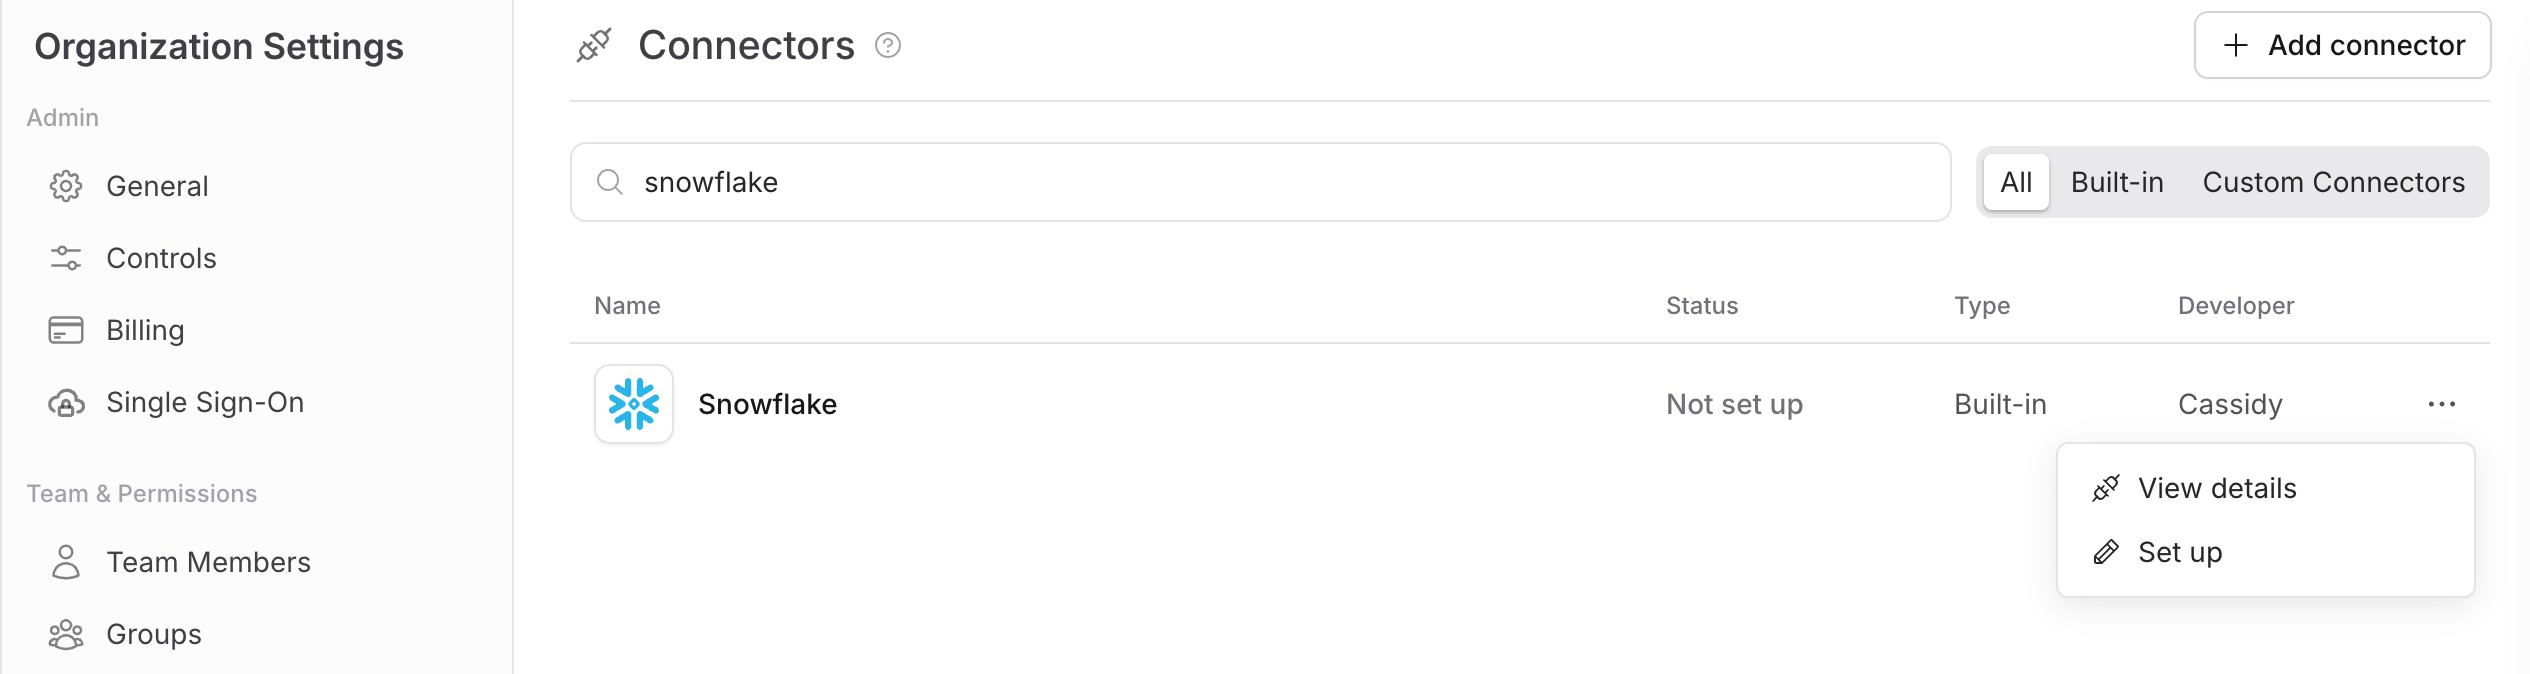
- A custom, confidential OAuth client.
- The exact Redirect URL shown in Cassidy’s setup dialog.
- Refresh tokens enabled so connections can renew without signing in for every query. Choose a refresh-token lifetime that meets your organization’s policy.
2
Save the organization configuration
Enter the Snowflake Account ID (for example, 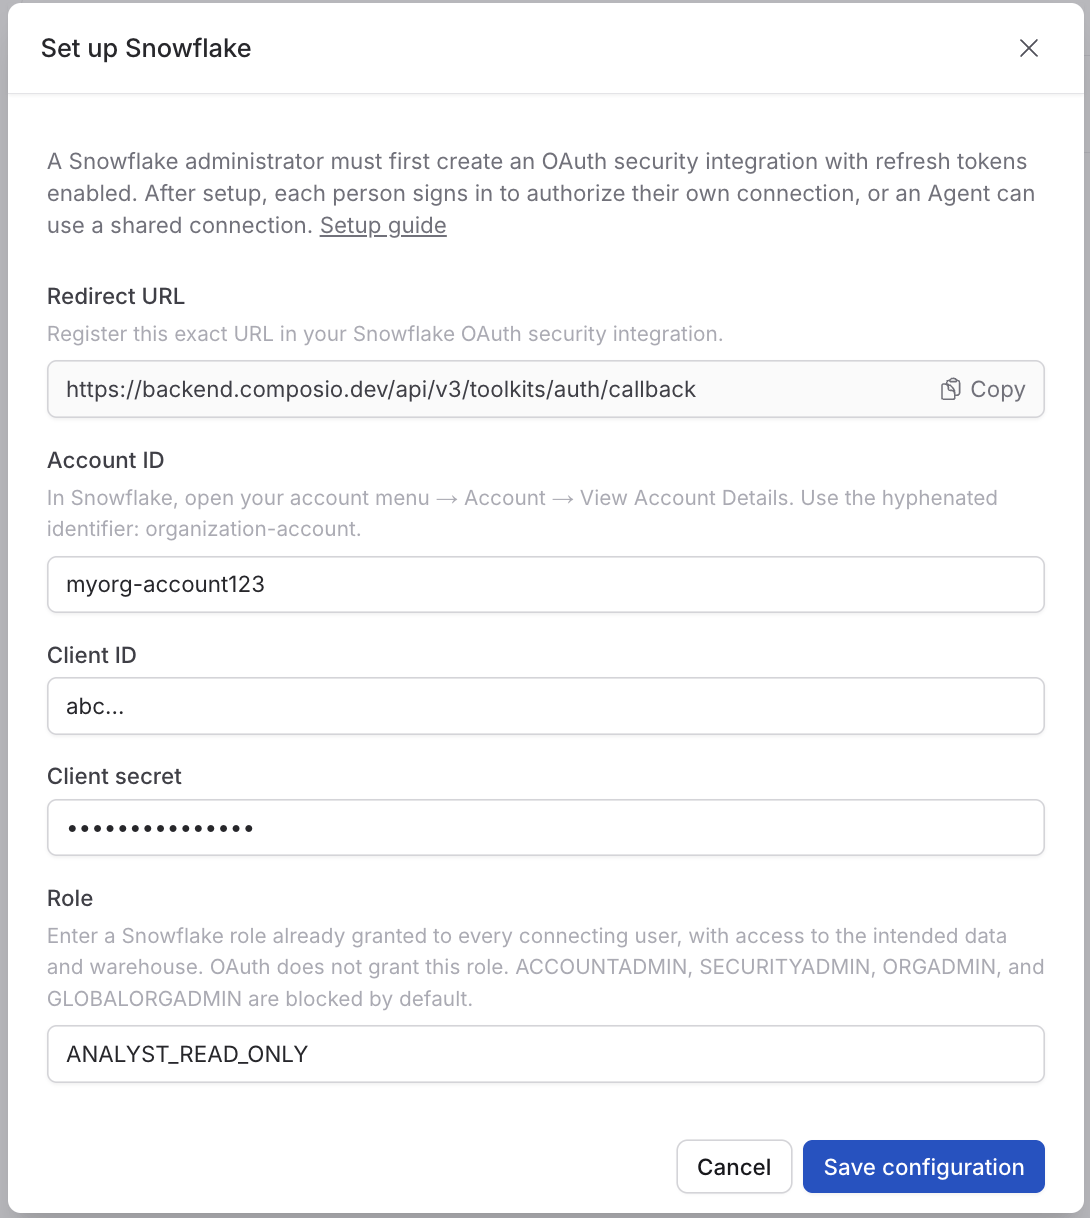
myorg-myaccount),
Client ID, Client secret, and Role in the Cassidy setup dialog.
Choose a role granted to connecting users with access to the intended data
and warehouse. Snowflake blocks ACCOUNTADMIN, SECURITYADMIN, ORGADMIN,
and GLOBALORGADMIN for OAuth by default. Select Save configuration.This makes the connector available unless your organization has separately
disabled it. It does not connect individual users yet. To rotate the client
secret later, choose Edit credentials. To change the account, client ID,
or role, delete the configuration and set it up again; all OAuth connections
will need to be recreated.3
Authorize a connection
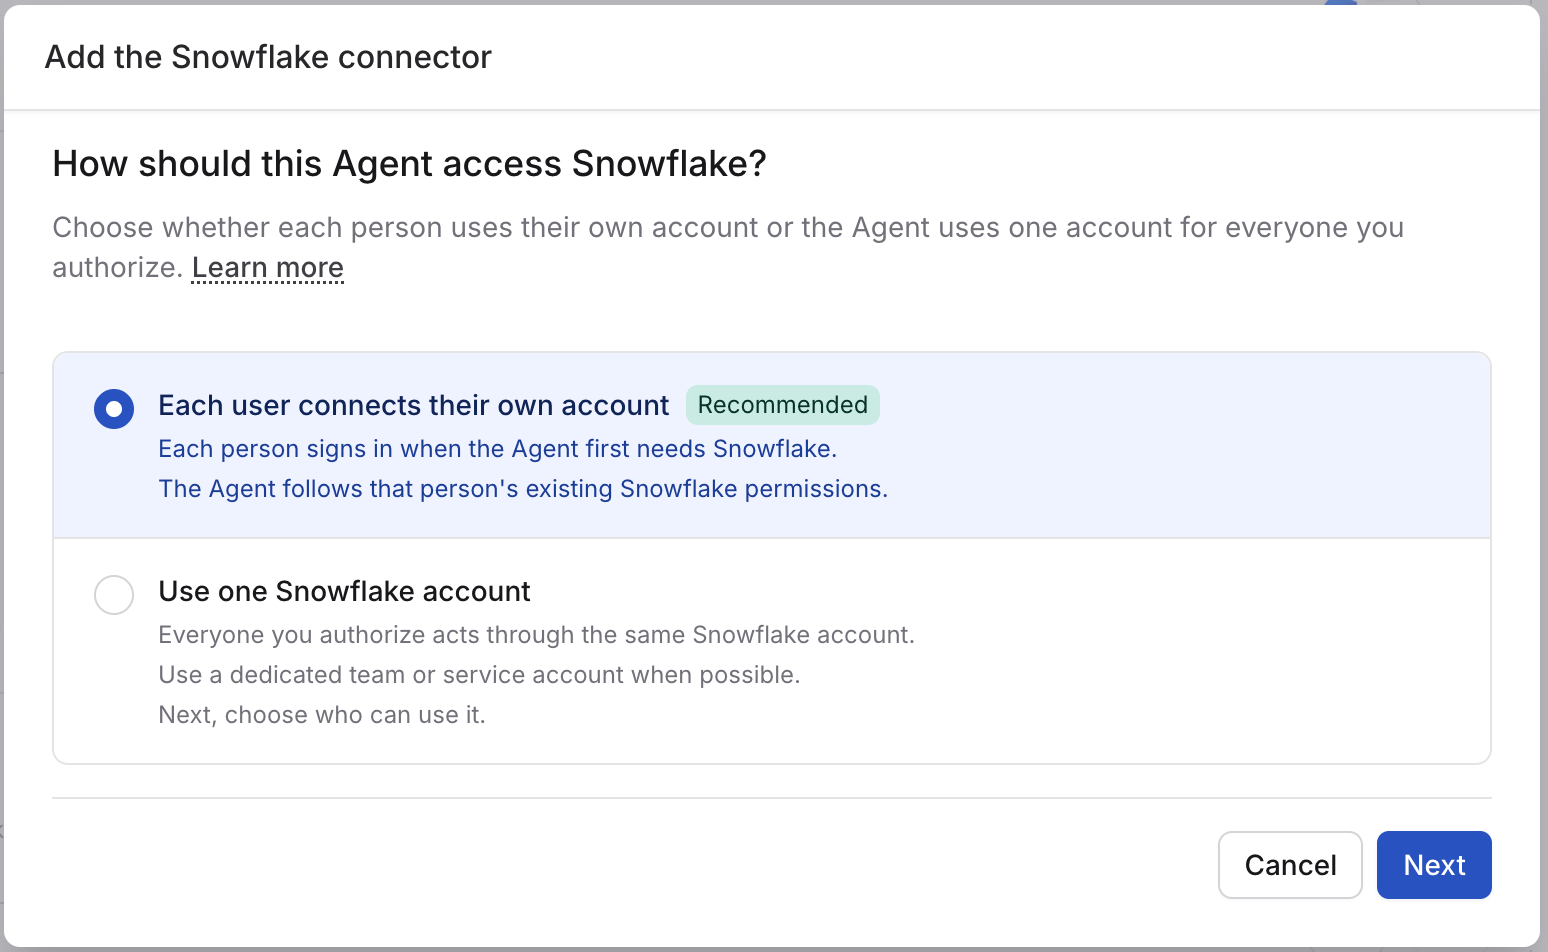
In Customize → Connectors, select Snowflake and Add connector.
Sign in to your organization’s Snowflake account, complete any required MFA,
and approve access.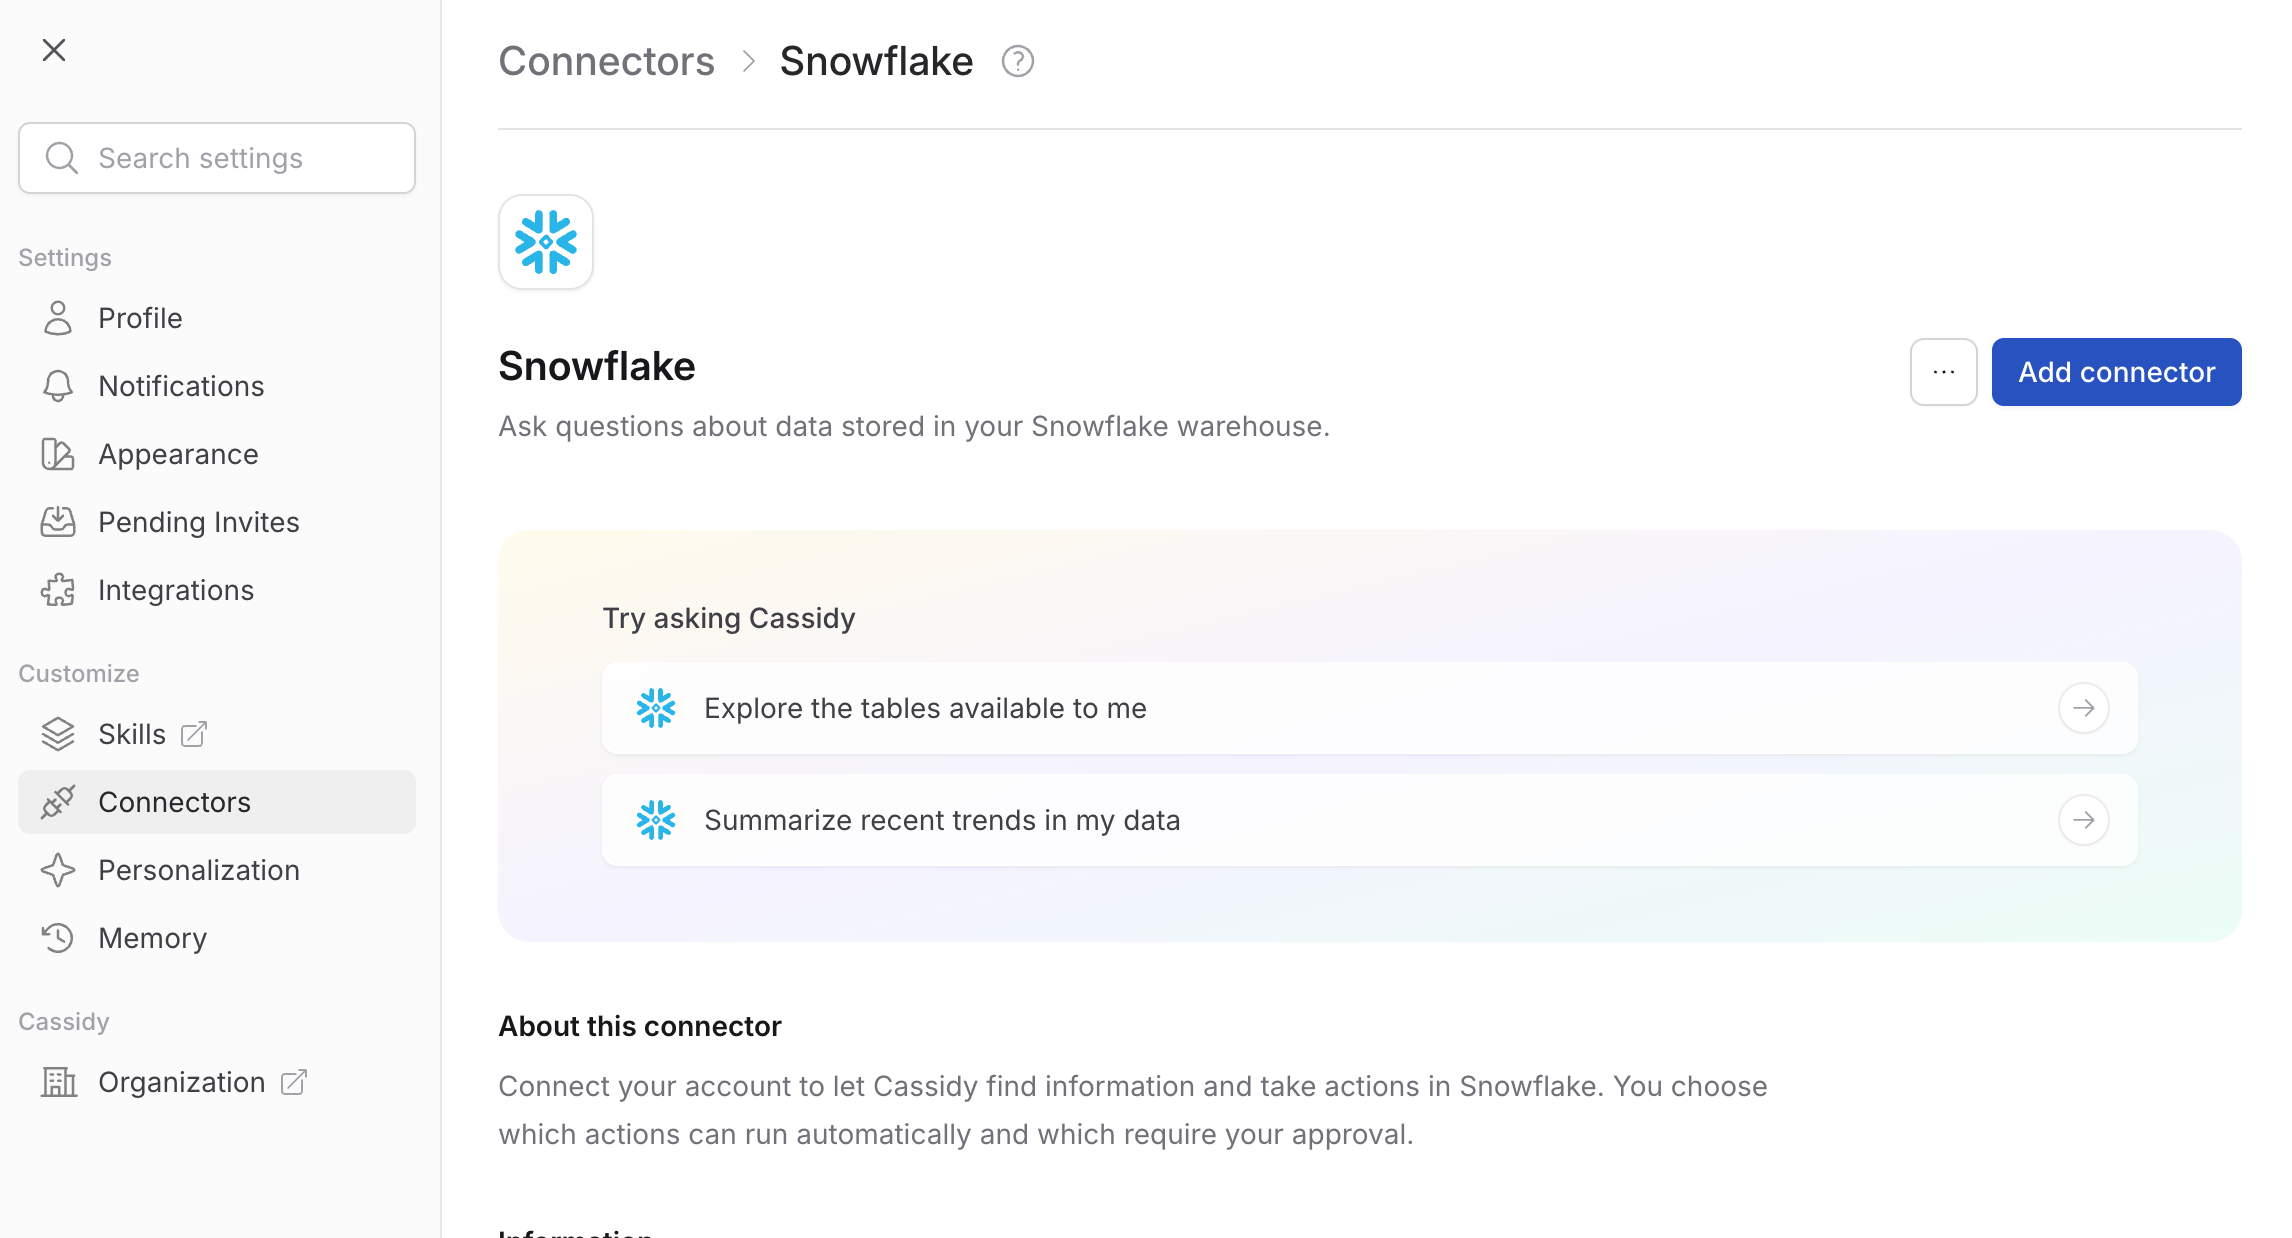
4
Choose actions and test your Agent
Enable the actions your Agent needs: Show Databases, Show Schemas,
Show Tables, and Run Read Query. SQL can also describe tables and
inspect columns. Run Write Query and Cancel Statement Execution are
disabled by default. Check Statement Status retrieves pending query
results and additional result partitions when needed.Select Add connector, then start a conversation with your Agent and ask
a question about your Snowflake data to confirm it can access the intended
tables.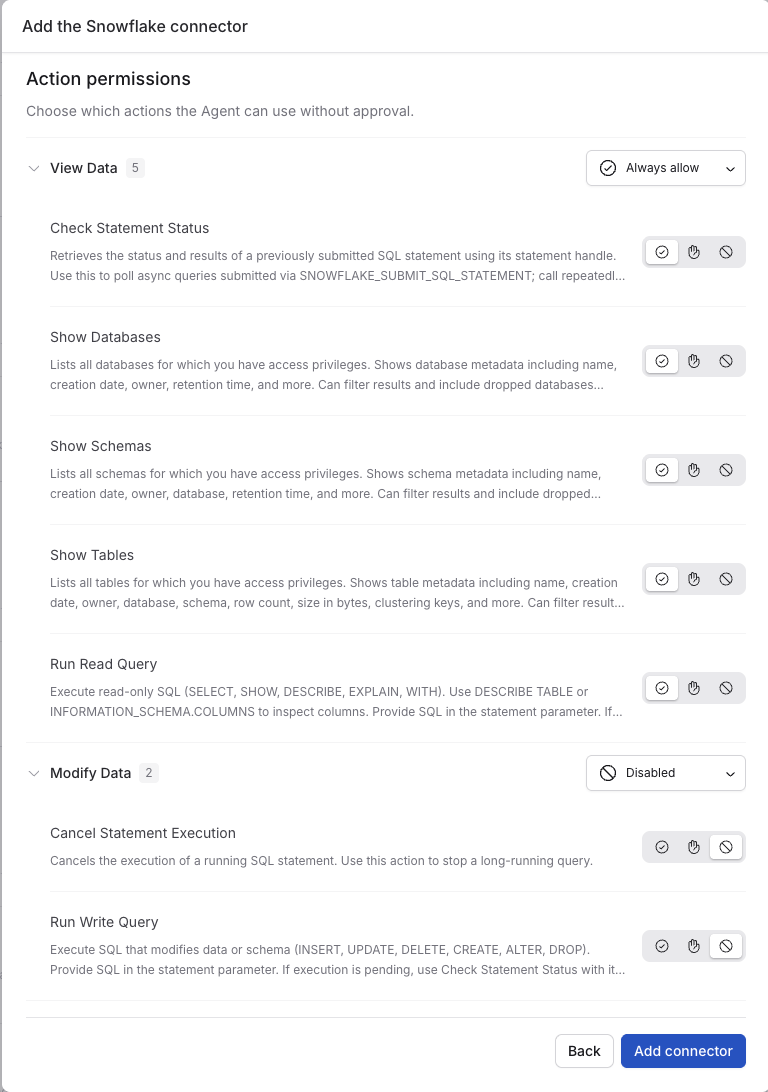
Connect Snowflake for yourself
To use Snowflake in any chat, not just with this Agent, open Customize → Connectors, find Snowflake, and click Add connector. See Add a Connector for yourself.Monitor Snowflake actions
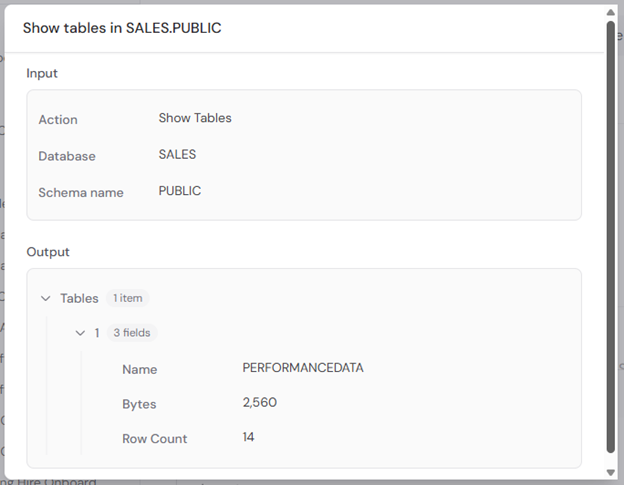
When an Agent uses the Snowflake Connector, expand the action in the response to see its input, result, and approval status.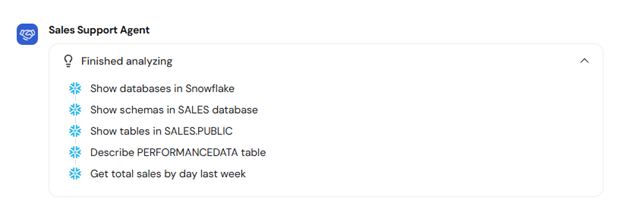
Data security
Snowflake data is accessed in real time and is not copied or stored in Cassidy. The Agent only queries Snowflake when needed to answer a question or complete a task.OAuth scopes
OAuth scopes
The Snowflake Connector requests access to run queries on the databases and
schemas you authorize. Cassidy does not access data outside the scope you
explicitly grant.
Next steps
Connectors overview
Learn about all available Agent Connectors and how they work.
Analyze data with an Agent
Combine Snowflake data with Code Execution & File Creation for deeper
insights.